While automated provisioning has made bringing UC and VoIP endpoints online faster and easier than ever, even highly automated systems can run into trouble when common provisioning pitfalls are overlooked. Knowing where those problems can occur and how to avoid them can mean the difference between a smooth rollout and a frustrating troubleshooting exercise.
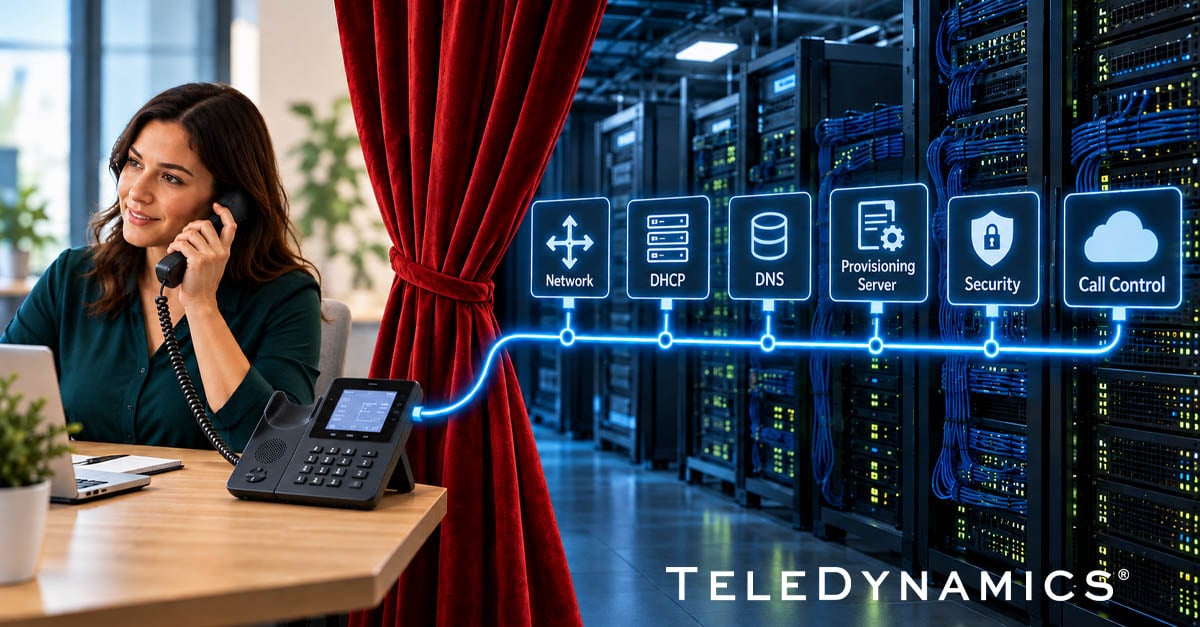
Behind the apparent simplicity of today’s provisioning systems lies a chain of network services, protocols, security mechanisms, and configuration dependencies that must all work together correctly. A problem at any point in that chain can prevent a device from provisioning or registering as expected.
In this article, we walk through the UC and VoIP provisioning process, highlighting common points of failure that even seasoned professionals may encounter and what to look for when things don’t go as planned.
The promise of zero-touch provisioning
Most of today’s UC and VoIP deployments boast easy provisioning with catchy marketing terms such as “low touch,” “no touch,” or “zero touch,” which indicate how much administrator involvement is required. Others use terms like “plug and play,” “turnkey,” or “functional out of the box,” meaning that you just have to plug in the endpoints and deploy the call control service (on an appliance or in the cloud) and you’re up and running.
In many cases, these claims are indeed true, and if we were to compare today’s available systems to those provided a decade ago, the difference is staggering.
The pitfalls of relying too much on automation
Mass provisioning is employed in multiple ways. It may be performed using proprietary mechanisms and vendor-specific management platforms. Alternatively, vendors may rely on standardized protocols and common network services for parts of the provisioning process. These may include standards such as TR-069/CWMP, configuration files commonly formatted in XML, DHCP options used to direct endpoints to provisioning servers, and protocols such as TFTP, HTTP, or HTTPS for retrieving configuration and firmware files.
The idea is that with the appropriate protocols and mechanisms, provisioning VoIP and UC systems today can become truly effortless.
Notwithstanding the benefits they provide, there can be risks in relying too heavily on automation and expecting it to function in all circumstances. There are cases where overconfidence in auto-provisioning capabilities has made them more of a pitfall than a boon.
Awareness of such pitfalls relies heavily on understanding the provisioning process that takes place when devices come online. The process is not the same for all devices. What we showcase here applies primarily to IP desk phones, but parts also apply to software voice clients and other UC endpoints. In any case, it gives a clear understanding of the potential points in the process where things can go wrong.
Auto-provisioning: what happens and where things go wrong
Devices typically go through the process of automation with the following steps:
discovery → network connectivity → provisioning-server discovery → configuration retrieval → authentication/security → firmware/configuration application → registration with call control.
Let’s take a look at what happens at each step and the potential points where things may go wrong. To start off, here is a table showing the types of processes that occur at each stage.
| Provisioning stage | Common pitfalls at this stage |
| Discovery |
Voice VLAN discovery |
| Network connectivity | DHCP, DNS, NTP |
| Provisioning-server discovery | DHCP options, DNS |
| Configuration retrieval | Provisioning-server reachability |
| Authentication/security | Certificates, secure provisioning, correct time |
| Firmware/configuration application | Compatibility, configuration precedence |
| Registration with call control | Device identity, stale provisionong records |
Discovery stage
When a voice device connects to a switchport, it will first discover the voice VLAN. This is done by using the standards-based Link Layer Discovery Protocol with Media Endpoint Discovery (LLDP-MED) or Cisco’s proprietary Cisco Discovery Protocol (CDP). Both of these link-layer discovery protocols tell endpoints which voice VLAN they should use. LLDP-MED/CDP must be enabled on the appropriate switchport if the endpoint relies on these protocols for voice VLAN discovery. Otherwise, registration may fail.
Network connectivity
This is where a device obtains its network parameters, including its IP address, subnet mask, default gateway, and DNS server. This is essentially the same for any DHCP-enabled end device, but there are a couple of important caveats for VoIP and UC devices.
DHCP is often used to inform endpoints about additional information, including the Network Time Protocol (NTP) server, a Trivial File Transfer Protocol (TFTP) server for downloading configuration files or firmware updates, SIP servers, and other vendor-specific parameters. These are conveyed via DHCP options, which are additional information included in DHCP messages sent to the end device. If these are misconfigured or missing, auto-provisioning may fail.
Related reading: Nine DHCP options that are particularly useful for VoIP and UC
Provisioning server discovery
Server discovery is tied to the DHCP options mentioned before, but here, we must make sure that the DHCP server serving the devices is configured with the appropriate IP addresses or domain names for the required servers. In addition, for domain names used to reach required services, the DNS server leveraged by the devices must contain the appropriate records for proper name resolution. For on-premises systems, DNS records should also exist for internally resolved domain names.
Configuration retrieval
Once the TFTP, HTTP, or HTTPS server used for configuration retrieval is learned via DHCP or another way, the device will search for that server to retrieve its configuration. This device is often the same entity as the call control server, but it doesn’t necessarily have to be. Devices will usually inform the server of their MAC address or another identifier and will be served with the configuration file, in XML format or otherwise, to obtain their specific parameters: phone number, allowed call types, and other capabilities and features.
Authentication and security
The configuration file may include parameters that aid device authentication as well as security features required for the device to communicate with central servers and other communication devices. This can include features such as security certificates and reliance on accurate time synchronization through NTP, which may be essential for time-sensitive security mechanisms
Firmware and configuration compatibility
A provisioning process can still fail at this stage even after the device has successfully reached the provisioning server and downloaded its files. Firmware versions, configuration templates, and device models must be compatible with one another. A configuration parameter supported by one firmware release may be deprecated, renamed, or interpreted differently by another.
Provisioned devices may obtain settings from several sources, including locally configured values, DHCP options, downloaded configuration files, and centralized management platforms. It is important to understand which source takes precedence. A manual change that appears to work may later disappear when the device reboots or performs its next provisioning cycle because the centralized configuration overwrites it. Whenever possible, make persistent changes at the authoritative provisioning source rather than directly on the endpoint.
Device identity and stale provisioning records
Identity is a key part of the provisioning process. Successful registration depends on the provisioning system and the call-control platform agreeing on the endpoint's identity. Elements such as MAC addresses, device names, extensions, user assignments, and other identifiers must correspond correctly. Problems can also arise when a replacement or previously used device encounters stale records associated with the old endpoint. When registration fails unexpectedly, verify both the device identity and any existing provisioning or registration records before troubleshooting the signaling itself.
Simplify provisioning with TeleDynamics
Of course, resellers and service providers don’t have to handle every aspect of device provisioning themselves. TeleDynamics offers provisioning services to help ensure devices are properly configured before they reach the customer, helping partners streamline deployments and reduce the time spent configuring endpoints in the field. Contact us for details.
Conclusion
Auto-provisioning has made UC and VoIP deployments faster and easier, but the simplicity that administrators see hides a complex chain of underlying services and dependencies.
When something goes wrong, understanding that process is essential. A misconfigured DHCP option, VLAN, DNS record, certificate, or provisioning entry can derail deployment and complicate troubleshooting. In UC and VoIP provisioning, understanding what happens behind the scenes is often the key to resolving problems quickly.
For partners looking to simplify the process, TeleDynamics offers provisioning services to help streamline device deployments. Contact us to learn more.
You may also like:
Simplify IP phone deployments with DHCP and LLDP-MED
Securing VoIP communications with SIP over TLS and SRTP
Minimize jitter, latency and other UC issues through proper routing


Comments